
Role Manager
Makaira ships with four default roles. Their names in the admin UI are Content Creator, Shop Manager, Administrator, and Owner. Internally they are stored as protected Makaira.* roles and cannot be edited or deleted.
Module access is decided by feature permissions (for example pageeditor.read). A user sees a dashboard tile when at least one of their assigned roles grants that permission. The tables below show the permission that gates each module and which default roles typically receive it.
Assign roles to people in User Management. Custom roles require the Role Manager module.
Typical default-role access
| Module | Permission | Content Creator | Shop Manager | Administrator | Owner |
|---|---|---|---|---|---|
| Page Editor | pageeditor.read | ✅ | ✅ | ✅ | ✅ |
| Advertising Banners | banner.read | ✅ | ✅ | ✅ | ✅ |
| Advertising Spaces | placement.read | ✅ | ✅ | ✅ | ✅ |
| Menu Editor | menu.read | - | ✅ | ✅ | ✅ |
| A/B Tests | abtesting.read | - | ✅ | ✅ | ✅ |
| Search | search.read | - | ✅ | ✅ | ✅ |
| Categories | categories.read | - | ✅ | ✅ | ✅ |
| Ranking Mix | rankingmix.read | - | ✅ | ✅ | ✅ |
| Personalization | personalization.read | - | ✅ | ✅ | ✅ |
| Recommendations | recommendations.read | - | ✅ | ✅ | ✅ |
| Redirects | redirects.read | - | ✅ | ✅ | ✅ |
| Smart Bundles | smartbundle.read | - | ✅ | ✅ | ✅ |
| Streams | streams.read | - | ✅ | ✅ | ✅ |
| Feeds | productfeeds.read | - | ✅ | ✅ | ✅ |
| Data Inspector | datainspector.read | - | ✅ | ✅ | ✅ |
| Category Mapping | categorymapping.read | - | ✅ | ✅ | ✅ |
| Tracking | statistics.read | - | ✅ | ✅ | ✅ |
| Index & Importer | indices.read | - | - | ✅ | ✅ |
| Settings | settings.read | - | - | ✅ | ✅ |
| Storefront Settings | storefront.read | - | - | ✅ | ✅ |
| Component Editor | component.read | - | - | ✅ | ✅ |
| Statistic | statistics.read | - | - | ✅ | ✅ |
| Audit Logs | auditlog.read | - | - | ✅ | ✅ |
| User Management | usermanagement.read | - | - | - | ✅ |
| Role Manager | usermanagement.read | - | - | - | ✅ |
| API Keys | secret.read | - | - | - | ✅ |
Write access uses the matching .write permission (for example pageeditor.write). Granting write always requires the corresponding read permission.
Booked feature flags still apply: a role can grant abtesting.read, but the A/B Tests tile only appears if that module is booked on the instance.
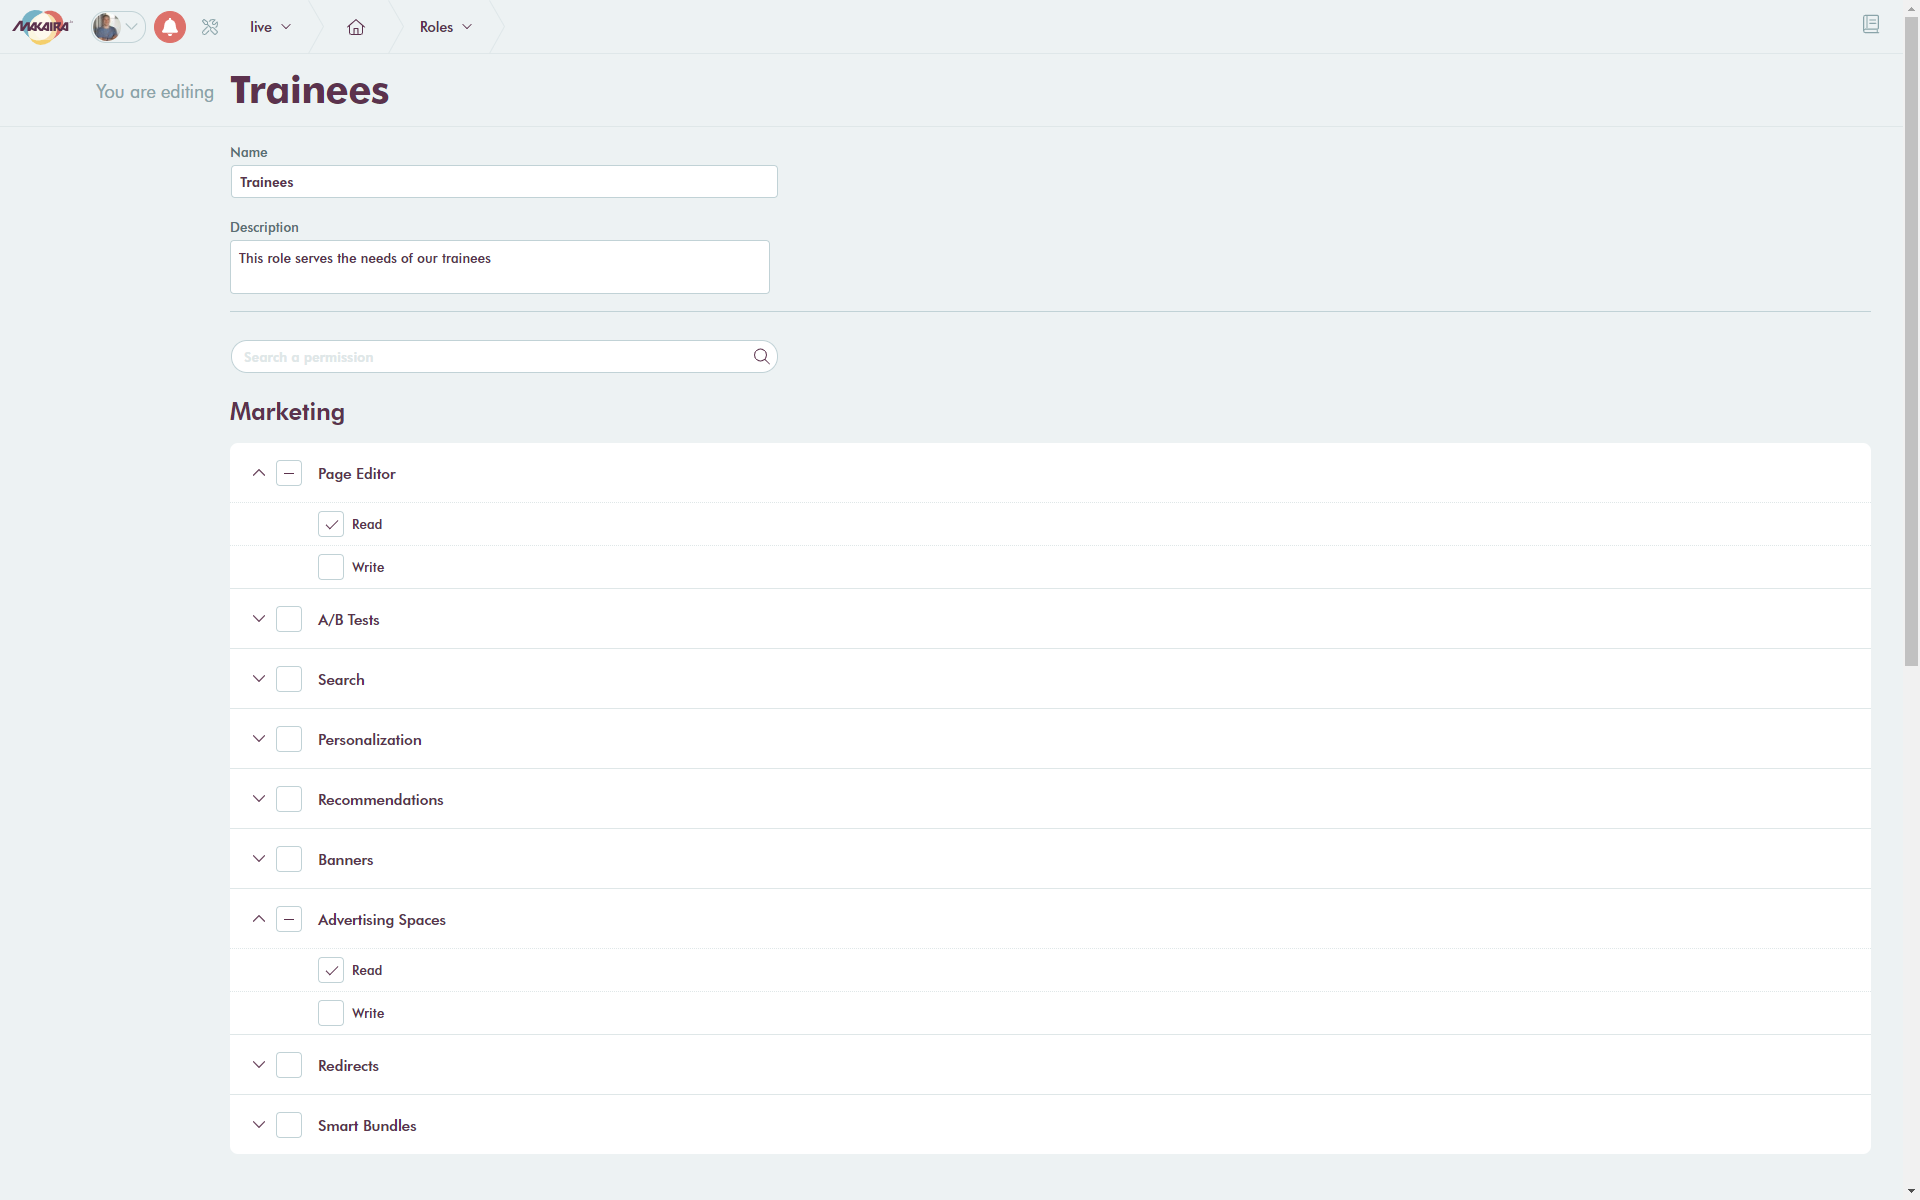
The Role Manager lets you create up to five custom roles with their own feature permissions, including access to installed custom apps ({app-slug}.read). Custom role names must not contain -- or __ (those separators are reserved for SSO group notation).
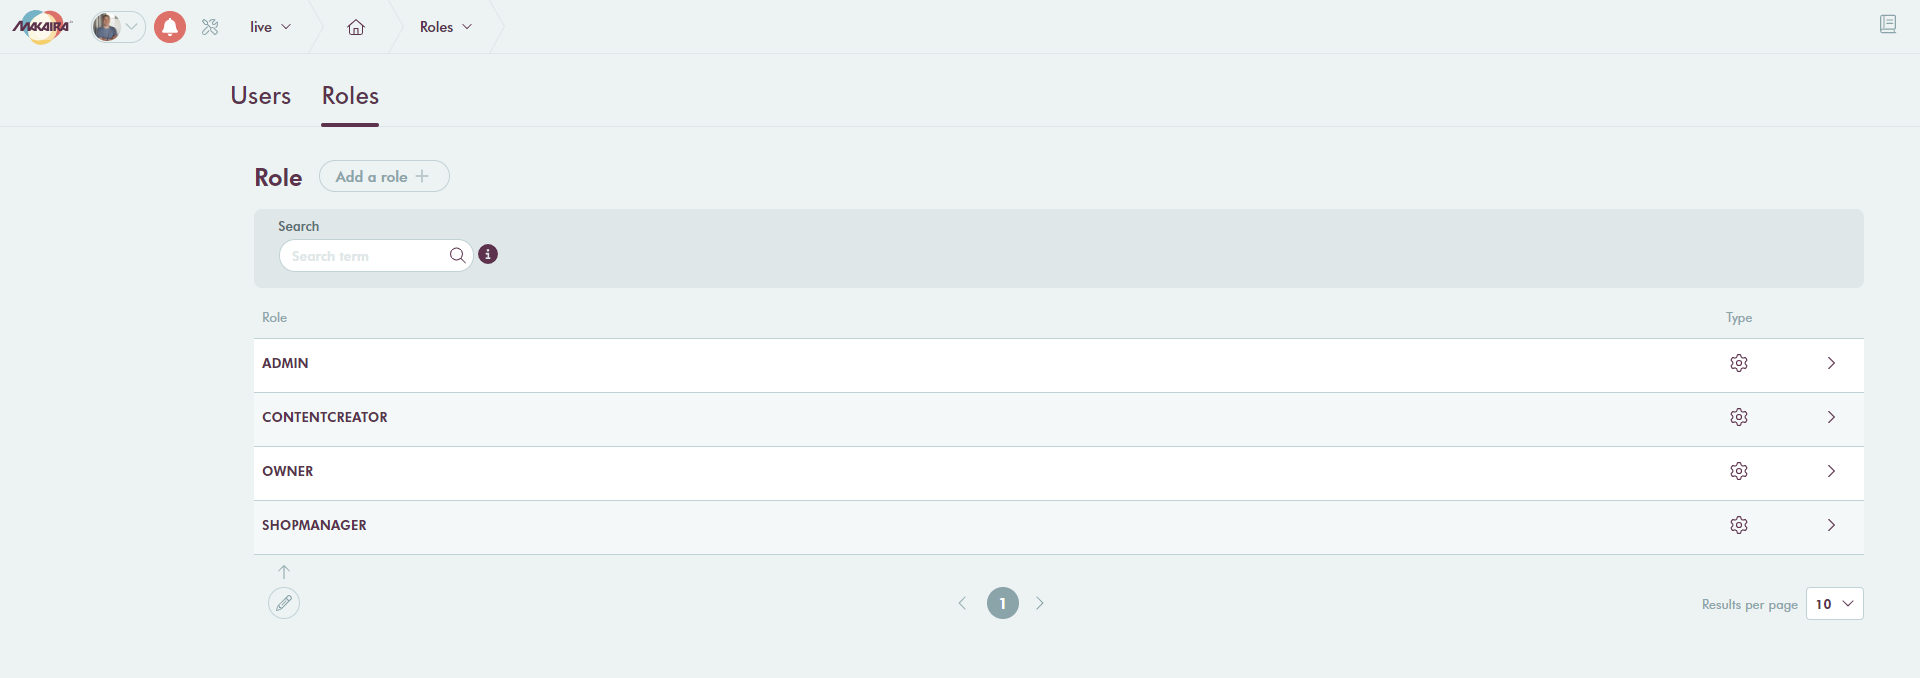
Creating a custom role
When adding a new role you define the name and the grants for that role. After you save it, assign it to users in User Management.
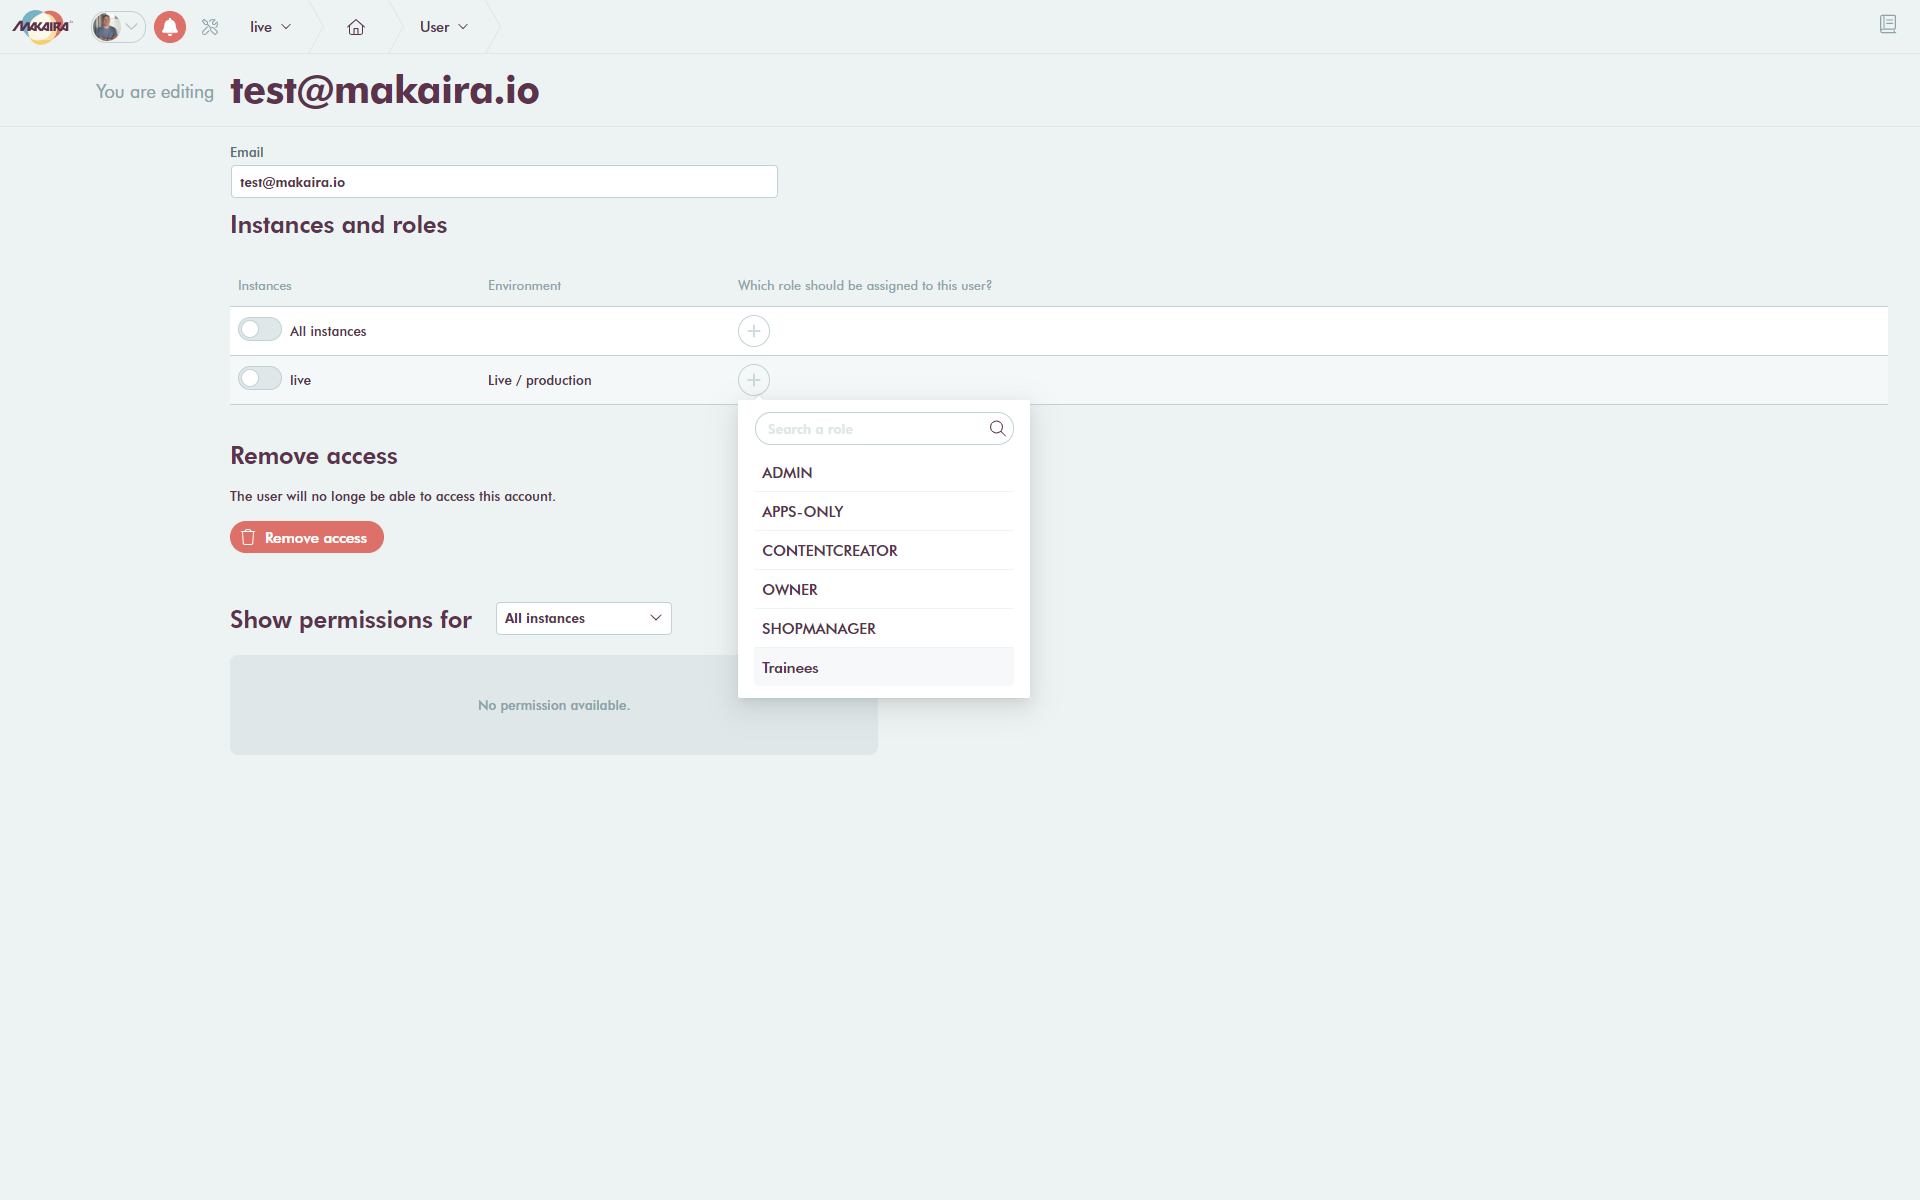
Assigning a role
Open the user in User Management, choose the instance, and select the role (default or custom).
Updated about 1 month ago